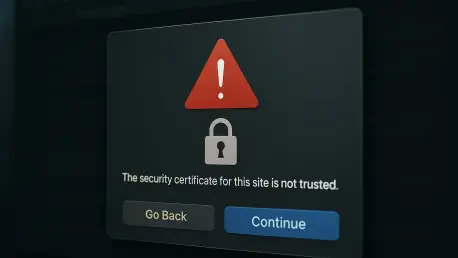
The digital landscape of 2026 continues to be reshaped by threat actors who have mastered the psychological manipulation of users through the very security protocols designed to protect them from harm. This trend is perfectly exemplified by the SilentDelivery campaign, a sophisticated cyberespionage operation that leverages counterfeit Google Chrome SSL certificate warnings to infiltrate high-profile targets. This campaign, attributed to actors with strong ties to established threat groups, does not rely on traditional vulnerabilities or zero-day exploits. Instead, it exploits the inherent trust that modern professionals place in their web browsers when navigating the complex security landscape of the internet. By hijacking legitimate domains belonging to government agencies, information technology firms, and research institutions, the attackers establish a foundation of perceived safety. This strategic subversion allows them to deploy backdoors like SquadC and SparrowDoor with a level of success that bypasses standard detection mechanisms.
Selective Targeting and Website Compromise
Selective targeting remains a cornerstone of the SilentDelivery operation, ensuring that high-value assets are identified before any malicious payload is ever delivered. The attackers begin by compromising the web infrastructure of reputable organizations across Asia and Europe, effectively turning trusted platforms into delivery vectors for espionage tools. Once access is gained, they inject highly obfuscated JavaScript, often processed through services like jsjiami, to monitor and filter incoming visitor traffic without raising suspicion. This code functions as a sophisticated gatekeeper, analyzing the digital footprint of every visitor to determine if they fit the profile of a desired target. By leveraging the existing reputation of these hijacked sites, the threat actors ensure that initial security scans by automated systems or cautious users are likely to return a clean result, as the underlying domain is entirely legitimate and recognized by global naming systems.
Furthermore, the fingerprinting process involves deep technical analysis of the visitor’s environment to verify specific criteria, such as the operating system and geographic location. The injected scripts are designed to verify that the target is running a Windows-based system, often communicating back to attacker-controlled infrastructure to confirm the victim’s IP address aligns with their strategic objectives. This level of precision prevents the unnecessary exposure of their malware to low-value users or security researchers who might be monitoring the network for anomalies. In some instances, the script even checks if the current domain matches a specific list of high-priority targets, ensuring that the heavy weaponry of their arsenal is only deployed when the potential for intelligence gain is at its peak. This disciplined approach to victim selection highlights a shift in modern cyberespionage, where the quality of the compromise is prioritized over the quantity of infections.
Mechanisms of the Fake Certificate Repair
The most distinctive feature of the SilentDelivery campaign is the “fake certificate repair” social engineering tactic, which presents a visually perfect imitation of a standard browser warning. When a targeted user navigates to a compromised page, the malicious JavaScript interrupts the session to display a notification stating that the connection is not private, mimicking the exact aesthetic of Google Chrome. Unlike legitimate browser errors that simply warn the user of a potential risk, this counterfeit interface includes a button labeled “Install certificate.” This prompt is meticulously crafted to exploit the user’s desire to maintain a secure and functional connection, making the act of clicking the button feel like a responsible security action rather than a dangerous mistake. By mirroring the behavior of a real SSL issue, the attackers successfully bridge the gap between technical deception and human psychology, leading the victim to download a malicious installer package disguised as a repair utility.
Once the user interacts with the “Install certificate” button, the delivery phase transitions to the deployment of specialized installers hosted on various Amazon S3 buckets. These installers are packaged as standard Windows executable files, further blending in with legitimate software maintenance tools that a professional user might encounter during a typical workday. The brilliance of this method lies in its feedback loop; after the malicious payload is successfully executed, the fake warning page disappears, and the user is granted access to the original website as if the “repair” had actually worked. This restoration of normal service serves to validate the user’s decision and significantly reduces the likelihood of the incident being reported to an internal IT department. By making the infection process appear as a successful resolution to a technical glitch, the threat actors maintain persistent access to the target environment while leaving the victim entirely unaware of the breach.
Backdoor Operations and Stealth Capabilities
At the heart of the infection lies the SquadC backdoor, a highly sophisticated piece of malware written in C/C++ that demonstrates advanced capabilities for stealth and persistence. SquadC utilizes a modular architecture, typically involving a three-stage loader that facilitates the injection of the core malicious code directly into the system’s memory. This fileless execution strategy is designed to minimize the physical footprint on the disk, making it extremely difficult for traditional antivirus solutions to detect the threat through standard file scanning. The backdoor is capable of performing a wide array of espionage activities, including the harvesting of sensitive system information, remote command execution, and the manipulation of local directories. Its design reflects a deep understanding of modern endpoint security, as the malware avoids many of the common triggers that would typically alert a security operations center to the presence of an unauthorized agent.
To ensure the longevity of their access, the developers of SquadC have integrated several anti-analysis features that allow the malware to detect and react to forensic environments. It can identify if it is running within a virtual machine or a sandbox used by security researchers, and it can be configured to remain dormant until specific conditions are met. For example, some variants are programmed to only remain active while a web browser process is running, effectively camouflaging their network communication as legitimate web traffic. This behavioral blending makes it nearly impossible to distinguish the command-and-control heartbeats from the background noise of standard organizational activity. Additionally, the malware’s ability to capture screenshots and log keystrokes provides the threat actors with a continuous stream of intelligence, allowing them to monitor the victim’s activities in real-time and adapt their strategies based on the information gathered from the compromised workstation.
Collaborative Infrastructure and Strategic Defense
Recent investigations into the infrastructure of these attacks have revealed a connection to a broader malware ecosystem managed by a centralized entity known as CopperDragon. This “digital quartermaster” appears to provide a unified supply chain for various China-linked threat groups, including FamousSparrow and TropicTrooper, sharing codebases and command-and-control techniques. By utilizing specialized tools like CopperDNS, which tunnels traffic through DNS queries to bypass firewalls, these groups maintain a resilient and adaptable network that is difficult to dismantle. The shared use of certificates and infrastructure across different operational clusters suggests a high level of coordination among these state-aligned actors, allowing them to rapidly iterate on their techniques. This collaborative environment enables the deployment of unique backdoors like SparrowShell for Linux systems, ensuring that no part of a target’s infrastructure remains safe from potential infiltration regardless of the platform.
The analysis of the SilentDelivery campaign demonstrated that the human element remained the most vulnerable link in the cybersecurity chain, even as technical defenses grew more robust. To counter these threats, organizations prioritized comprehensive user training that emphasized the inherent dangers of in-browser software prompts. It was established that genuine security updates and certificate management were never conducted through manual downloads from third-party websites, but rather through integrated system protocols. Security teams shifted their focus toward endpoint detection and response tools that could identify memory-based injection techniques and anomalous DNS tunneling patterns. By fostering a culture of skepticism regarding unexpected security warnings and implementing strict application control policies, defenders successfully mitigated the risks posed by such deceptive social engineering tactics. The campaign served as a critical reminder that maintaining a proactive and informed workforce is just as essential as deploying the latest technical safeguards.