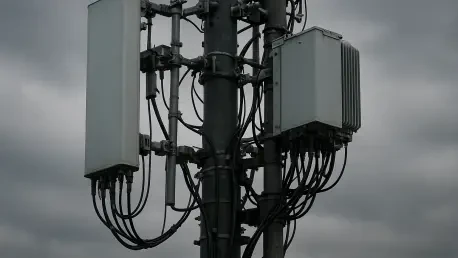
Strategic defense against foreign interference is driving the EU to treat cybersecurity as a critical component of utility infrastructure and medical device safety. This shift has placed the removal of high-risk 5G telecommunications equipment at the forefront of the regional legislative agenda, sparking intense debate between central regulators and individual member states. The European Commission initially advocated for a strict and uniform 36-month phase-out period for all hardware provided by vendors deemed a security risk, specifically targeting international giants from outside the bloc. However, this rigid timeline met significant resistance from national governments that preferred a more flexible, risk-based approach tailored to their unique economic and technical landscapes. The current standoff highlights a fundamental challenge within the Union: how to secure critical digital infrastructure without imposing a financial burden that could cripple the very operators tasked with building the future of European connectivity and digital services.
Navigating Economic Realities and Implementation Timelines
The current debate over telecommunications security is inextricably linked to the immense financial and logistical pressure facing the European mobile market. While the strategic goal of reducing reliance on high-risk vendors is widely accepted, the practical execution of this goal requires a delicate balance between national security and economic stability. Central to this issue is the recognition that the telecommunications sector serves as the backbone for the entire digital economy, and any mandated changes must be technically feasible and financially sustainable. Regulators are now forced to consider whether a rigid, one-size-fits-all deadline is the most effective way to achieve security, or if a more nuanced approach would better serve the long-term interests of the bloc. This transition represents a significant pivot from the idealistic mandates of previous years toward a more pragmatic implementation strategy that acknowledges the diverse needs of individual member states.
Balancing Financial Stability: The Economics of Security
The debate over implementation timelines is deeply rooted in the economic reality of modern telecommunications, where the cost of a forced transition remains a primary concern for major network operators. Industry leaders, including prominent names like Orange and Deutsche Telekom, have projected that a rapid replacement of existing 5G infrastructure could require a combined investment of approximately €40 billion across the continent. These organizations warned that such an aggressive capital drain would inevitably stall other vital technological projects, such as the ongoing expansion of high-speed fiber-optic networks and the early research phases of 6G development. By advocating for a more extended timeline, member states argued that they could align equipment replacement with the natural lifecycle of hardware, thereby minimizing financial waste. This approach suggested that security mandates should not exist in a vacuum but must consider the long-term financial health of the digital economy to remain viable.
Technical Hurdles: Replacing Integrated Infrastructure
Beyond the financial implications, the technical complexity of overhauling established mobile networks presented a significant logistical barrier to a rapid 36-month phase-out. European networks are not monolithic structures but rather intricate, multi-generational systems where components from different eras and manufacturers must work in perfect harmony to provide stable service. In countries where equipment from certain vendors is deeply integrated into the existing 4G and 5G layers, such as Germany and Italy, a forced premature removal could lead to catastrophic service disruptions or complete network failures. To address these concerns, a stratified strategy was proposed, which focused on the immediate replacement of high-priority core components while allowing peripheral or less critical hardware to remain until its scheduled obsolescence. This nuanced methodology aimed to preserve the integrity and reliability of the mobile experience while gradually reducing the presence of high-risk technology.
Establishing a Differentiated Path Forward
A broader shift toward digital sovereignty is reshaping how the Union approaches its long-term security architecture and supply chain dependencies. This evolution is characterized by a move away from fragmented national policies toward a more cohesive and harmonized European framework that prioritizes the resilience of critical infrastructure. By viewing digital security as a strategic asset, the bloc is seeking to reduce its vulnerability to external geopolitical pressures and ensure that its communication networks remain under domestic or trusted control. This strategy is not merely about excluding certain vendors but about fostering a robust and diverse technological ecosystem that can withstand future disruptions. The ongoing legislative updates reflect a growing consensus that true sovereignty requires a proactive and comprehensive plan that addresses both technical vulnerabilities and the broader risks associated with the geopolitical influence of third-country suppliers.
Geopolitical Risks: Assessing Vendor Influence
Geopolitical considerations have fundamentally altered how the European Commission evaluates the risks associated with foreign technology suppliers, shifting the focus from technical flaws to political leverage. While early security assessments prioritized identifying specific software vulnerabilities or hardware backdoors, the current methodology emphasizes the broader risks linked to the influence of third-country governments over their domestic companies. This evolution in perspective allowed regulators to treat certain vendors as high-risk not just because of their code, but because of the potential for their equipment to be used as a tool for strategic dependence or espionage. In contrast, affected vendors maintained that these measures were discriminatory and lacked empirical technical evidence, arguing that their equipment met all international security standards. This conflict underscored the difficulty of crafting a policy that balanced legitimate national security interests with the principles of fair competition.
Pragmatism in Practice: Insights for Future Stability
The resolution of these debates ultimately established a pragmatic path forward that favored a differentiated timetable over a one-size-fits-all approach. Regulators recognized that for the transition from 2026 to 2028 and beyond to be successful, they needed to provide operators with clear, predictable roadmaps rather than sudden ultimatums. This historical shift allowed member states to implement security measures at a pace that matched their specific infrastructure needs and economic conditions. Future-proofing efforts then turned toward diversifying the supplier base, encouraging the adoption of Open RAN technologies and other interoperable solutions that reduced the risk of vendor lock-in. By prioritizing the most sensitive parts of the network first, authorities managed to enhance the regional security posture while ensuring that the broader digital transformation remained on track. This strategy demonstrated that effective cybersecurity required a long-term commitment to technical excellence and strategic autonomy.