The Ministry of Communications is under increasing pressure to resolve network latency and speed issues as the government transitions essential services to local infrastructure. This mandate comes at a pivotal moment when the state is aggressively pursuing a doctrine of “managed sovereignty” to insulate its digital borders from perceived external interference. Under the guidance of the Supreme Council of Cyberspace, the nation has accelerated the deployment of its domestic ecosystem, viewing the global internet not merely as a utility but as a primary theater for hybrid conflict. This paradigm shift prioritizes the fortification of national security interests over the seamless global connectivity that characterized earlier technological eras. By framing the current digital environment as a space of constant geopolitical friction, the government justifies a proactive stance that involves both defensive shielding and offensive signal management. This overarching strategy aims to create a robust, independent network that can withstand systemic pressure.
Neutralizing Satellite Interventions and Legal Challenges
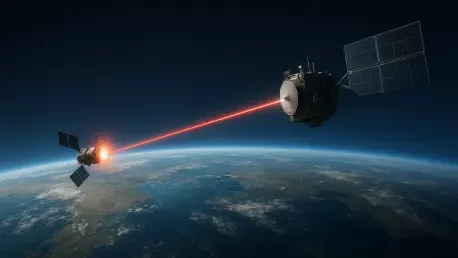
The sudden ubiquity of low-Earth orbit satellite services, particularly SpaceX’s Starlink, has prompted a vigorous response from Iranian technological specialists who view these systems as unregulated conduits for external influence. Recent reports indicate that the state has successfully engineered advanced signal-processing tools capable of identifying and neutralizing individual satellite terminals within its borders. During the domestic unrest observed late last year, official sources claimed that approximately 80% of data packets transmitted via these satellite networks were effectively disrupted, rendering the remaining bandwidth insufficient for functional use. Unlike traditional GPS jamming, which often causes broad collateral interference, the new strategy utilizes targeted protocols to intercept the direct communication link between orbiting transmitters and ground-based receivers. This technical capability is presented as a necessary response to the unauthorized deployment of hardware that bypasses domestic regulatory frameworks.
Complementing this technical interference is a sustained diplomatic and legal offensive coordinated through the International Telecommunication Union and other global regulatory bodies. The Ministry of Communications has consistently argued that the operation of foreign satellite constellations within its airspace constitutes a violation of established sovereignty and international telecommunication laws. By filing formal complaints and issuing warnings to nations associated with the regulatory processing of these firms, such as Norway and the United States, Iran seeks to force a standard of operator compliance with the laws of host nations. The core of this legal argument rests on the assertion that satellite internet is a dual-use technology, citing its utilization in foreign conflicts for military command-and-control, drone navigation, and intelligence gathering. This classification allows the state to frame its opposition not as a restriction of civilian communication, but as a legitimate defensive measure against tools that potentially facilitate espionage.
Cyber Warfare and the Doctrine of Hybrid Confrontation
The Iranian leadership has increasingly adopted a military-centric view of the digital landscape, defining it as a front in a “hybrid war” that integrates physical, economic, and psychological dimensions. This doctrine is predicated on the observation that modern military engagements are almost always preceded or accompanied by a significant surge in cyberattacks against national infrastructure. In the current year, security agencies have documented an escalation in distributed denial-of-service attacks and sophisticated social engineering campaigns targeting essential utilities and government databases. While the majority of these attempts have been contained by the national firewall, officials acknowledge that attackers have reached their objectives in limited instances, prompting a reevaluation of defensive protocols. In response, the state advocates for a policy of “limiting access routes” during periods of heightened tension, a strategic euphemism for severing international traffic to isolate the domestic network from foreign hackers.
Much of the current defensive posture is rooted in the long-lasting impact of historical events like the Stuxnet attack, which remains a cornerstone of the national argument for digital isolation. This legacy of sabotage has fostered a deep-seated institutional distrust of foreign hardware and software, leading to the implementation of rigorous filtering mechanisms designed to strip away “amateur” digital noise. By narrowing the field of incoming data, cybersecurity teams can more effectively concentrate their resources on identifying and neutralizing high-level threats that originate from professional, state-backed entities. During recent periods of heightened geopolitical friction, such as the widely discussed “12-day war” scenario, authorities demonstrated the ability to disconnect international access during the final stages of the conflict to secure the domestic landscape. This approach reflects a strategic belief that total control over data flow is the only viable method for ensuring the integrity of critical infrastructure systems.
The National Information Network and Digital Autonomy
A central pillar of this drive for autonomy is the National Information Network, which has recently reached an estimated 60% completion rate, marking a substantial increase from its development levels in the preceding several years. The primary objective of this massive infrastructure project is to decouple essential services—including the banking sector, national healthcare databases, and educational platforms like the Shad system—from the global internet backbone. By ensuring that these services operate on a localized loop, the government aims to guarantee that the country remains functional even if external connectivity is severed by sanctions or technological warfare. Despite this progress, official assessments admit that significant shortcomings still exist, particularly regarding domestic search engine capabilities and the availability of large-scale cloud computing resources. Addressing these gaps has become a national priority, with increased funding directed toward local tech startups that can provide domestic alternatives to foreign-hosted platforms.
To enhance the long-term viability and public acceptance of this domestic ecosystem, the Supreme Council of Cyberspace has implemented a series of mandates aimed at improving network quality and institutional security. The Ministry of Communications was recently tasked with resolving the persistent latency issues and speed bottlenecks that have historically plagued local connections, acknowledging that poor network performance is a major barrier to digital self-sufficiency. Furthermore, the state has introduced a mandatory cybersecurity assessment framework for high-priority institutions, starting with universities and national banks. These organizations are now subject to rigorous security audits, with a grace period provided to rectify vulnerabilities before the results are made accessible to the public. This push for transparency is intended to build public trust in the reliability of domestic platforms while reducing the reliance on foreign software that could contain hidden backdoors, ensuring that the network remains resilient.
Future Directions: Securing the Digital Landscape
The transition toward a fully autonomous digital infrastructure represented a fundamental shift in how the state managed its relationship with the global information highway. By prioritizing the development of the National Information Network, authorities successfully insulated vital government and financial sectors from the volatility of international cyber warfare. This strategy moved beyond simple reactive measures, establishing a comprehensive framework where domestic digital platforms became the primary choice for both citizens and institutions. The systematic identification and disruption of unauthorized satellite signals demonstrated a clear intent to enforce territorial boundaries within the electromagnetic spectrum, effectively curbing the influence of foreign technology providers. As the government finalized its 32-point resolution for filtering reform, it sought a balance that maintained security without stifling the growth of the local tech industry. Moving forward, the focus turned toward ensuring the superior quality of localized services.
The implementation of rigorous cybersecurity audits served as a final safeguard, ensuring that the transition to local infrastructure did not compromise the safety of sensitive national data. Organizations that previously relied on foreign cloud services began migrating to domestic alternatives, bolstered by state incentives designed to accelerate the growth of the internal digital economy. This shift was accompanied by a renewed focus on technical education, with the government aiming to produce a new generation of specialists capable of maintaining and evolving the National Information Network. By fostering a self-contained environment, the state mitigated the risk of external sabotage while providing a stable foundation for the future of digital commerce and governance. These actions established a precedent for other nations seeking to reclaim control over their digital borders in an increasingly fractured global landscape. The emphasis shifted from mere containment to the active cultivation of a technological ecosystem that prioritized national resilience above all else.