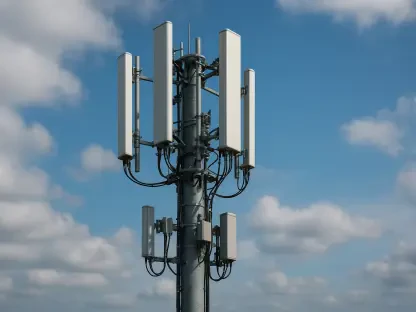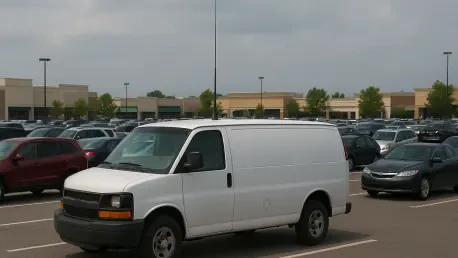
Mobile network operators including BT, Vodafone, and Virgin Media O2 collaborated with law enforcement to track down the source of the unauthorized transmissions. This unprecedented investigation led to the conviction of Mohammed Faiyaz Iqbal, a 43-year-old resident of Preston, who deployed a highly sophisticated “SMS blaster” to exploit vulnerabilities in mobile communication. By concealing a portable mini cell tower inside a standard van, Iqbal was able to bypass traditional security protocols and transmit fraudulent messages directly to mobile devices in the vicinity. This marks a significant escalation in local cybercrime, as it represents the first recorded instance where United Kingdom law enforcement successfully identified and dismantled hardware-based smishing infrastructure. The operation allowed the perpetrator to act as a localized network provider, effectively hijacking the digital trust of thousands of citizens without alerting legitimate carriers. These rogue towers broadcast at high power to force nearby phones to disconnect from legitimate masts and reconnect to the malicious source.
Signal Exploitation: The Mechanics of Rogue Interception
The core of this operation relied on the deployment of a rogue base station, a device often referred to in technical circles as an IMSI catcher or an SMS blaster. These units mimic the behavior of a legitimate cellular tower, broadcasting a signal that appears more attractive to a mobile device’s internal roaming logic than the signals coming from authentic masts. Once a device establishes a handshake with this unauthorized equipment, the perpetrator gains the ability to push malicious content directly to the user’s interface. This technique, known as smishing, leverages the inherent trust users place in SMS communication. Unlike email, which is often filtered by robust spam algorithms, direct text messages delivered via localized hardware bypass many of the modern cloud-based defenses used by service providers. This allows criminals to impersonate trusted brands such as Royal Mail or financial institutions with a terrifying degree of perceived authenticity, tricking victims into clicking malicious links.
During the apprehension of Iqbal at the Trafford Shopping Centre, the Dedicated Card and Payment Crime Unit discovered a complex array of hardware integrated into the vehicle’s structure. The setup featured high-gain aerials mounted on the roof, powered by internal battery banks and managed through mobile applications. Upon searching the suspect’s mobile devices, investigators found 7,859 unique and compromised payment card details, indicating that the localized smishing attacks were highly effective in harvesting sensitive financial information from unsuspecting citizens. Furthermore, the discovery of counterfeit driver’s licenses suggested a broader intent to facilitate identity theft and money laundering. This evidence pointed to a comprehensive criminal pipeline where stolen data was immediately funneled into secondary fraud systems. The ability to collect thousands of data points in a single afternoon highlights why these devices became a priority for law enforcement. This specific case served as a critical warning regarding the evolution of mobile fraud.
As the technological landscape shifted, it became clear that individuals and organizations needed to adopt more proactive security postures to mitigate the risks posed by rogue hardware. The most effective actionable step for users during this period was the adoption of encrypted messaging platforms that did not rely solely on traditional SMS protocols, which remained inherently vulnerable to interception. Additionally, enabling multi-factor authentication that utilized app-based tokens or hardware keys rather than SMS-based codes provided a critical layer of defense even when a rogue tower intercepted a message. For the telecommunications industry, the focus for the period from 2026 to 2030 remained on the widespread deployment of 5G security enhancements that mandated mutual authentication between the device and the network. These measures significantly diminished the effectiveness of IMSI catchers by requiring a cryptographically signed handshake that rogue towers could not easily replicate, ensuring that the private information of mobile users remained secure in a complex environment.