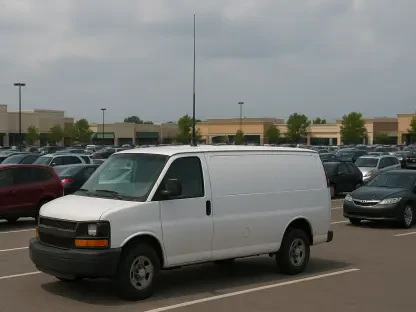
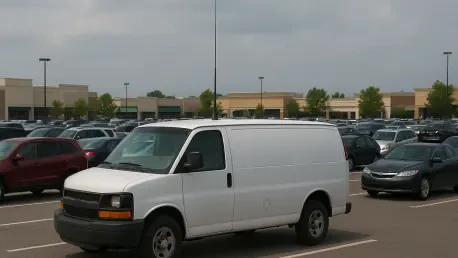
Mobile network operators including BT, Vodafone, and Virgin Media O2 collaborated with law enforcement to track down the source of the unauthorized transmissions. This unprecedented investigation led to the conviction of Mohammed Faiyaz Iqbal, a 43-year-old resident of Preston, who deployed a
Administrators must verify their LiteSpeed versions and review privileged account activity to ensure no backdoors were created prior to applying the urgent security patch. This high-priority alert follows the discovery of a critical vulnerability in LiteSpeed Web Server Enterprise that effectively
The global landscape of artificial intelligence is rapidly evolving into a fractured map of digital territories where national interests dictate the development of localized computing power. Many telecommunications companies currently outsource their AI capabilities to global giants to minimize
Industry analysts suggest that a strategically timed transition period would allow operators to replace aging Chinese gear during standard upgrade cycles, significantly reducing redundant costs. The digital landscape of India is undergoing a fundamental reconfiguration as the government intensifies
Deploying the BridgeAgent backdoor on Linux management hosts allows actors to blend into standard enterprise operations by masquerading as legitimate monitoring processes like the Zabbix agent software. This subtle infiltration marks a significant evolution in the tactical playbook of the threat
Corporate security teams now face a reality where only 44 percent of organizations remain free from follow-up attacks within thirty days of an initial cyber incident. This data indicates a significant transition in the threat landscape, where attackers prioritize quality and persistence over the
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35